
Colombia Ranks Among Top 30 Markets for Online Gambling Participation
DataReportal figures put monthly online gambling participation at 13.8% of Colombian internet users aged 16 and over, behind Brazil and Chile in South America.
This website contains information about gambling and betting and is intended for adults only. You must be at least 18 (or the legal age in your country) to enter.
Gambling can be addictive. Please play responsibly.
WhiteArmor claims to have stolen records covering 15.4 million Gamdom accounts, but the alleged database and a published sample have not been independently authenticated.
An extortion group calling itself WhiteArmor is demanding $15 million from crypto casino Gamdom over an allegedly stolen database containing 15.4 million player accounts.
The group reportedly published records relating to 100 accounts as purported evidence. Their authenticity remains unconfirmed, and Gamdom has not publicly confirmed or denied the alleged database theft.
Threat-monitoring services recorded Gamdom’s appearance on WhiteArmor’s leak site on October 26. Such listings document a criminal group’s claim rather than independently establish that a breach occurred or that the advertised data is genuine.
According to Dark Web Informer’s account, WhiteArmor says it accessed Gamdom’s management panels and stores containing passwords and keys through an internal service account with administrative privileges.
The attackers claim the account had existed for several years without its login credentials being changed. No independent technical investigation has substantiated that explanation.
WhiteArmor also made allegations about Gamdom’s provably fair games, claiming they did not function as advertised. The group supplied no supporting evidence for that assertion.
The extortion claim emerged 13 days after a confirmed attack on Gamdom’s hot-wallet infrastructure.
Gamdom suspended operations on October 13 after discovering an unauthorised connection to an automation server. Founder Felix Römer subsequently put losses at just over $3 million, while blockchain investigator vxdb estimated approximately $4.2 million. The operator said remaining hot-wallet assets had been moved into cold storage and that customer funds were safe.
The website resumed operations on October 16.WhiteArmor has not explicitly connected its alleged database theft to the wallet incident, so the timing alone does not establish a shared attacker or access route.
WhiteArmor began appearing in public threat-monitoring records in October. WatchGuard categorises it as a data broker, while other monitoring services describe its activity as data-theft extortion.
The reported demand, claimed account count and alleged access method remain unverified. Confirmation of the earlier wallet theft does not authenticate the new database claims.
DataReportal figures put monthly online gambling participation at 13.8% of Colombian internet users aged 16 and over, behind Brazil and Chile in South America.
WhiteArmor claims to have stolen records covering 15.4 million Gamdom accounts, but the alleged database and a published sample have not been independently authenticated.
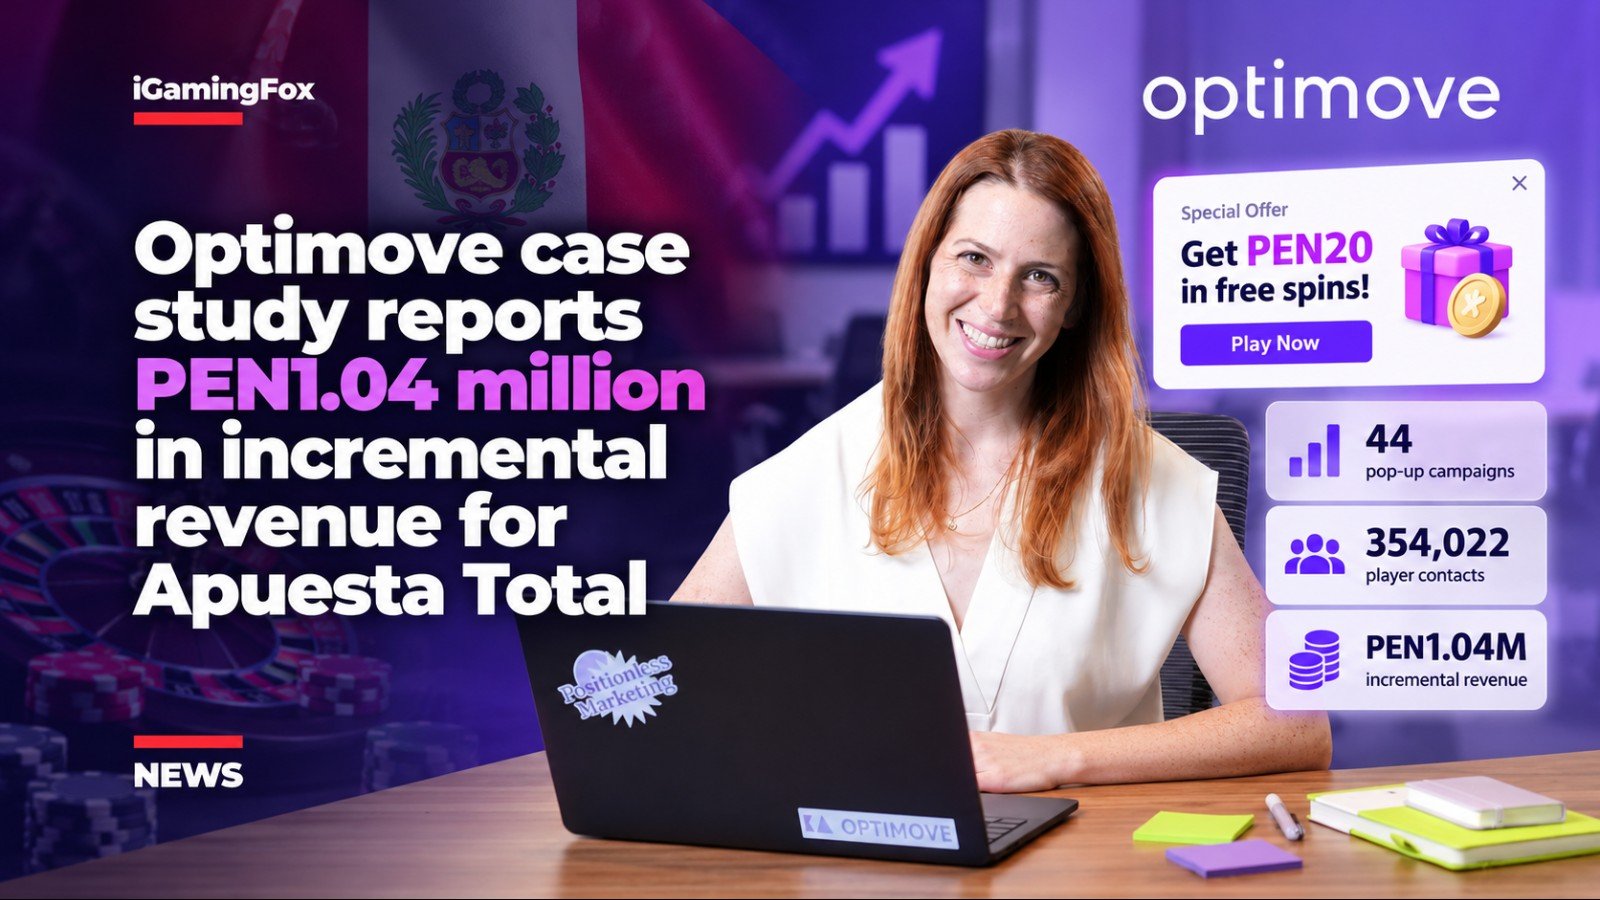
Apuesta Total’s 44 triggered campaigns generated reported incremental revenue of approximately $303,000, although Optimove’s case study leaves key measurement and cost details undisclosed.
The National Police Board has received 79 applications and issued 12 licences without rejecting any, as operators prepare for Finland’s competitive online gambling market.

Breaking iGaming news, bonuses and event alerts — straight to your phone.
Join the channel
Comments (0)
No comments yet. Be the first!